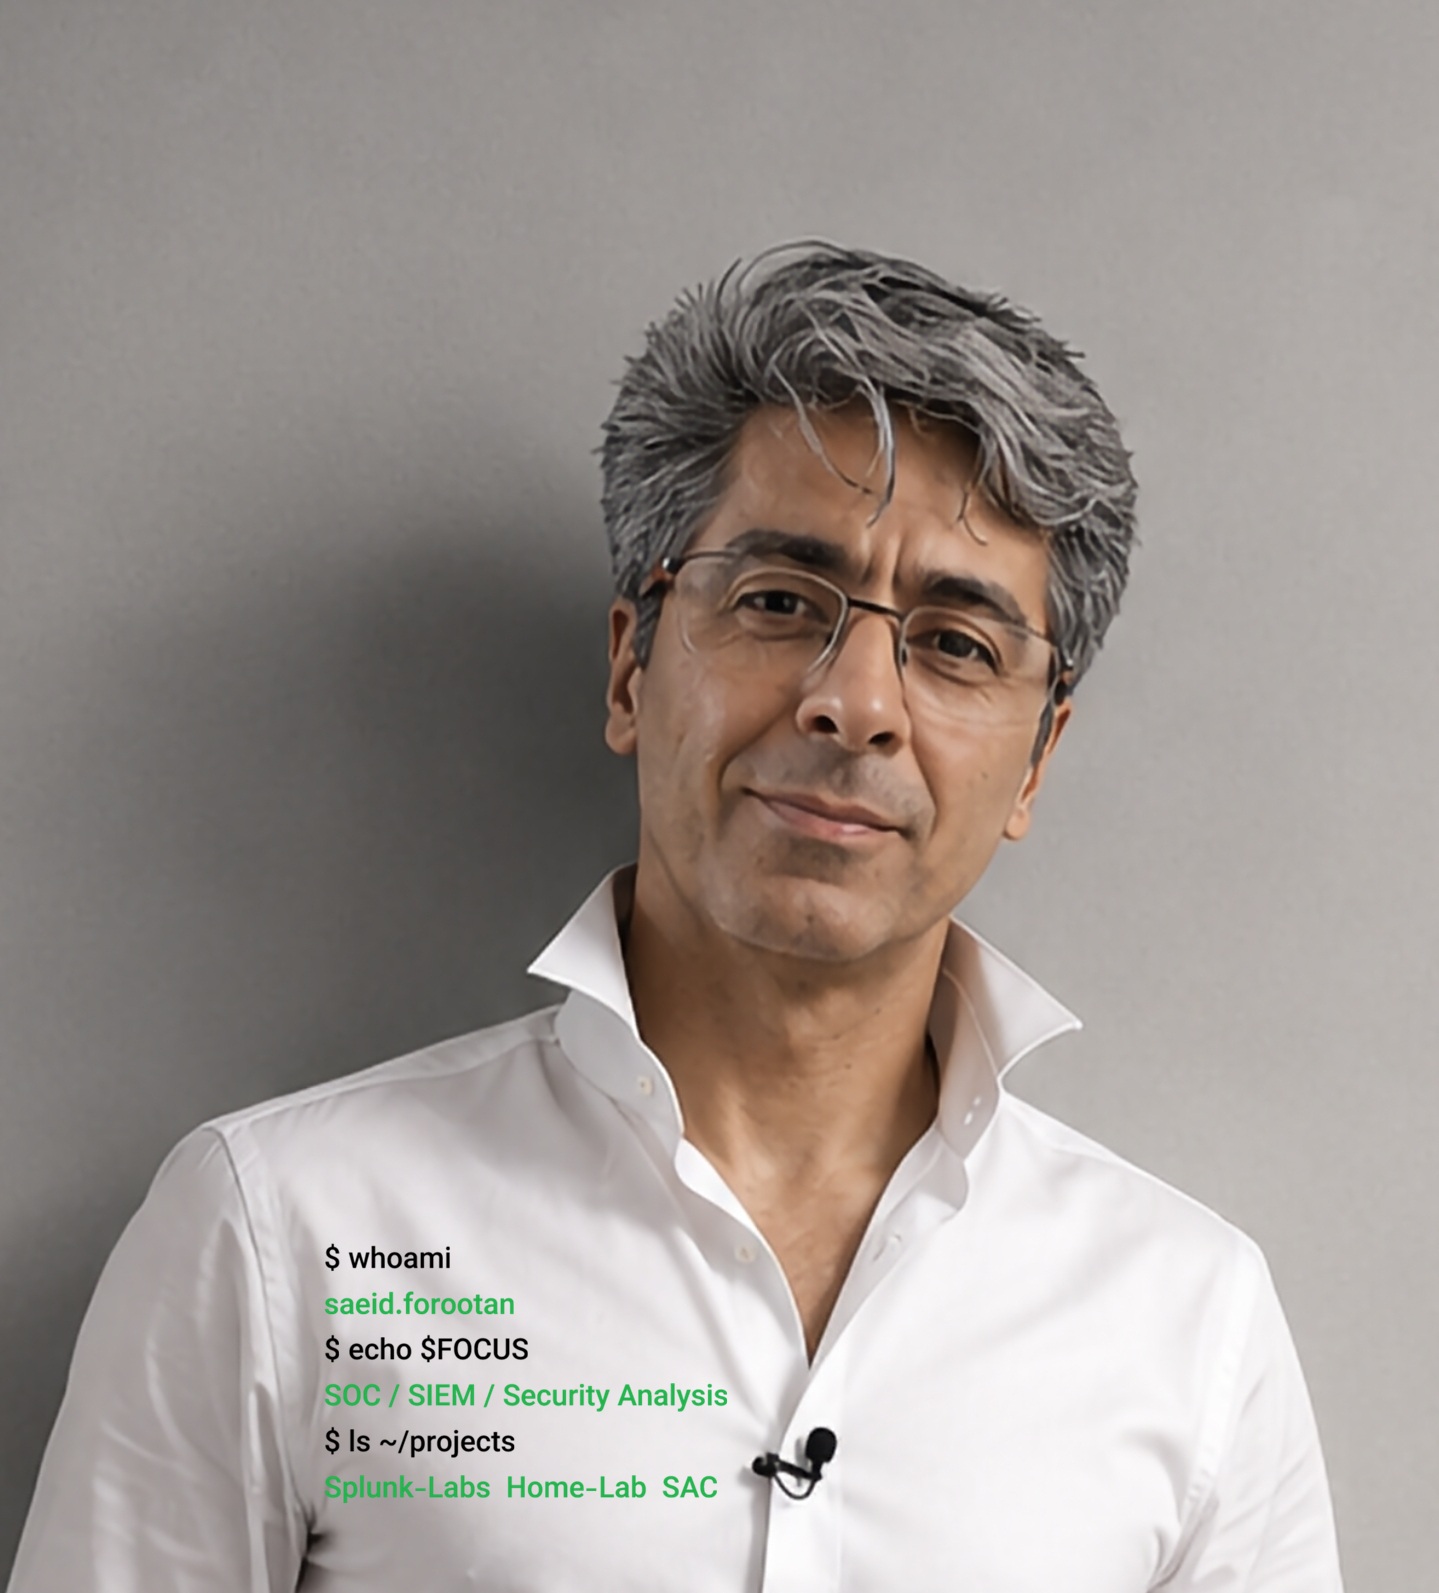
Saeid Forootan
FA
Splunk Enterprise
Wazuh
Windows Event Logs
Sysmon
Active Directory
PowerShell
Networking
SPL